Dave Ochoa

Security Operations Executive CISSP Associate C|CISO

Security that enables the business.

I'm Dave Ochoa. For 15+ years I've built and run security programs in regulated environments, unifying messy, federated infrastructures into operations that hold up in front of boards, auditors, and attackers.

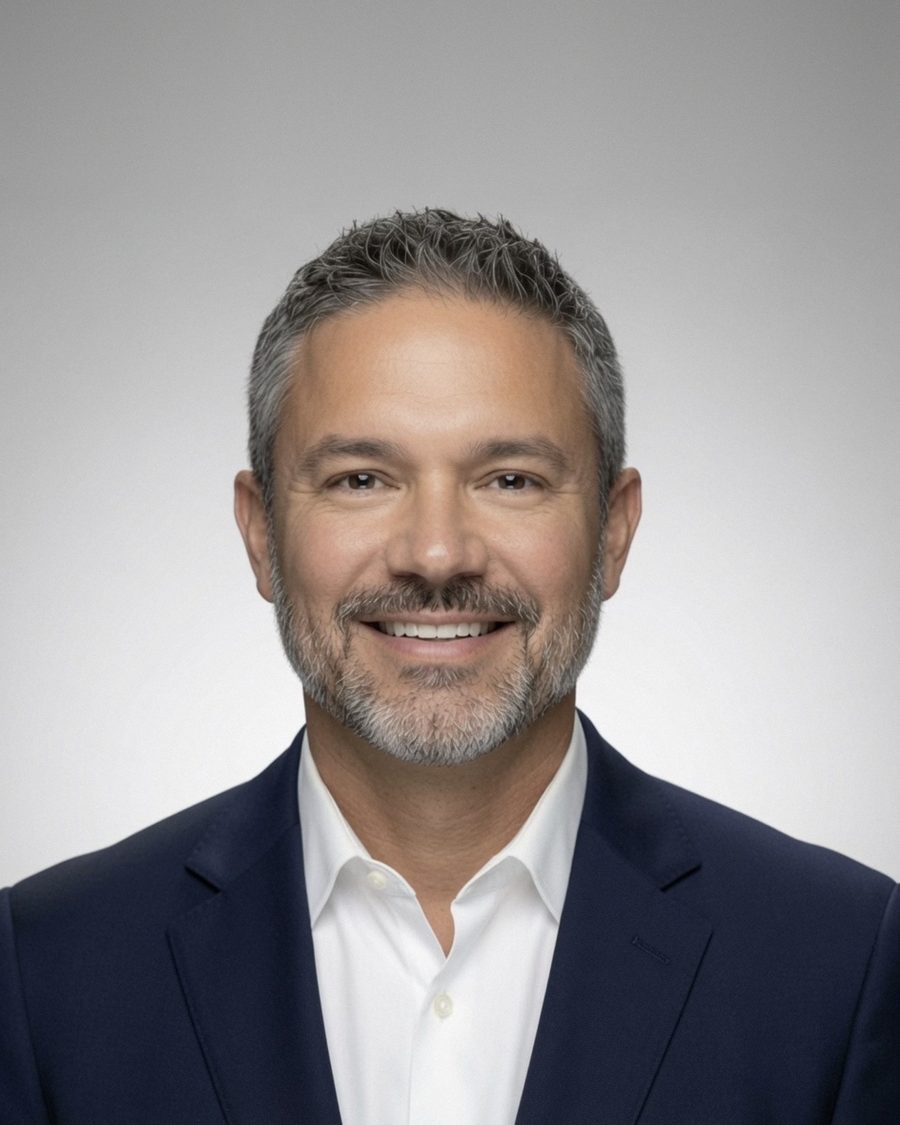
Portrait of Dave Ochoa
15+ years in security and infrastructure
75M+ patient records protected
15K systems secured across multi-cloud
4 acquired companies unified under one security operation

About

I build and run security operations programs in regulated environments. Most recently that meant leading global SecOps at HealthEdge, where the CISO brought me in to centralize security across four acquired healthcare SaaS companies: 75M+ patient records, 15K systems, and a 13-person team spanning the US and India. We consolidated four legacy security programs onto a single SIEM/SOAR platform, accelerated vulnerability remediation by 60 days, and built the technical controls behind the company's AI governance program.

Before that I spent a decade at Apria Healthcare, moving from Security Architect to Manager to Director. I built their first in-house SOC from scratch, drove containment time down over 95% through automation, and drove remediation time for critical vulnerabilities from 90 days to under 30.

The through line: I take messy, federated environments and turn them into measurable security programs. Hands-on enough to own the platforms (QRadar, Sentinel, CrowdStrike, Netskope, Tenable), senior enough to brief a board.

Track record

FusionNode

Head of Architecture and Operations, 2024 - 2025

Founding technical leader for a Zero Trust and SASE managed-security startup. Built the architecture and operations functions from inception, led an 8-person team serving five enterprise clients, and saw the company through its US wind-down in November 2025.

HealthEdge

Senior Director of Information Security Operations

Recruited by the CISO to centralize security across four acquired healthcare SaaS companies. Led a 13-person global SecOps team, consolidated four legacy security programs onto one SIEM/SOAR platform, achieved SOC 2 attainment with controls benchmarked against ISO 27001 and NIST CSF, and built the technical controls behind the company's AI governance program.

Apria Healthcare

Architect to Manager to Director

Built Apria's first in-house SOC from inception. Reduced containment time by over 95% through automation, stood up a three-part threat hunting program mapped to MITRE ATT&CK, led the Zero Trust segmentation redesign across Azure and hybrid infrastructure, and as Director owned HIPAA, PCI, and HITRUST controls with quarterly reporting to the Board and Audit Committee through IPO preparation.

Earlier career

Telecommunications and OT, 2003 - 2015

Global telecom engineering across 21 sites in 13 countries, and early hands-on ICS work: designed and built an HMI/SCADA monitoring system on industrial hardware years before OT security became an industry discipline.
Credentials

CISSP Associate C|CISO
  • Certified Information Systems Security Professional (CISSP), ISC2, active since 2018
  • Associate Certified Chief Information Security Officer (Associate C|CISO), EC-Council

Regulatory depth

HIPAA HITRUST PCI DSS SOC 2 NIST CSF

Let's talk.

I'm currently exploring Director, VP, and CISO-track roles in healthcare, SaaS, and other regulated spaces. If you're building a security program that needs to enable the business rather than slow it down, I'd welcome the conversation.

Orange County, CA. Open to remote and hybrid.